Based in Kigali, working across Africa
Offensive security & penetration testing for Africa's regulated institutions
Manual VAPT for banks, fintechs, telecoms, government and healthcare, with evidence-led reports structured for BNR supervision.
Or take our free 3-minute security score quiz and see your score at once.
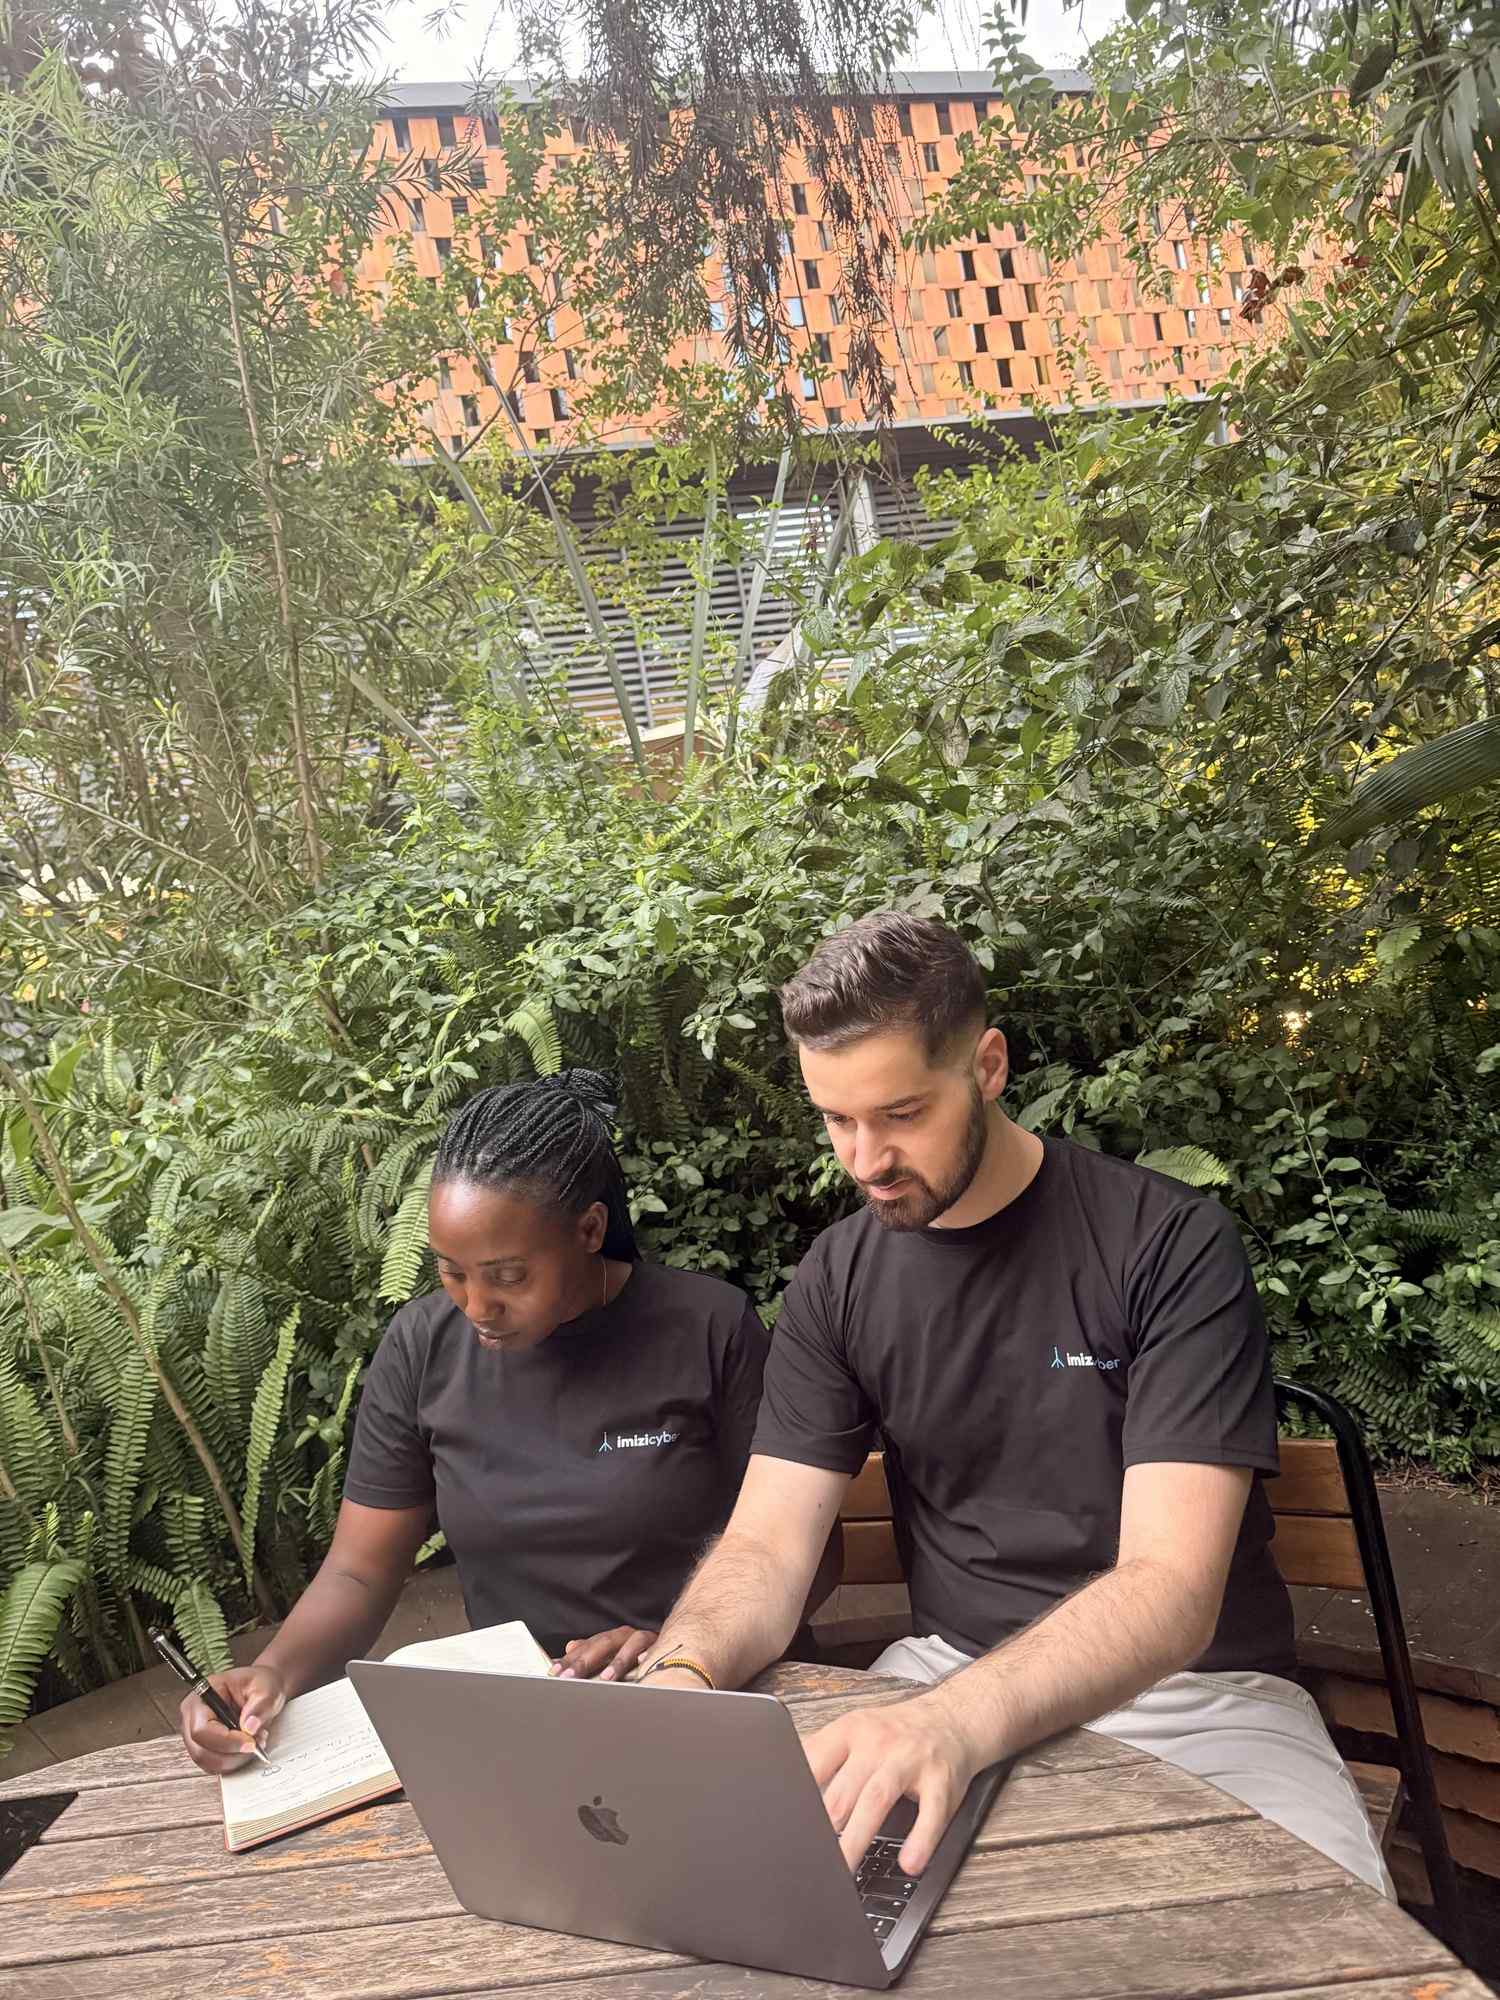
The team behind the testing
Our testing is led by an OSCP-credentialled practitioner, and the person who tests your systems writes your report.

Aristofanis Chionis Koufakos
Lead Penetration Tester
Aristofanis Chionis holds the OSCP, co-presented the open-source Honeyscanner tool at Black Hat Europe 2023 Arsenal, and brings red-team and penetration-testing experience from Nordic and pan-African banking, plus an MSc in Computer Security.
Credentials
- Certification OSCP Offensive Security
- Certification PNPT TCM Security
- Conference talk Black Hat Europe 2023 Arsenal Co-presented Honeyscanner, London
- Open source Honeyscanner Top contributor, GSoC 2023 with the Honeynet Project
- Degree Computer Security Technical University of Denmark
- Degree Informatics & Telecommunications NKUA
Why choose IMIZI Cyber
Manual testing, confirmed by exploitation
We confirm every finding by exploiting it by hand, and we test directly for the business-logic flaws, chained issues and access-control gaps that scanners miss.
Evidence-led reports, written by hand
The person who ran the test writes the findings and the remediation guidance, with reproduction steps your engineers can follow and a summary your management can act on.
Red-team experience from banking
Our lead practitioner comes from threat-led red-team work at a Tier-1 Nordic bank and penetration testing across pan-African banking. We test your systems the same way.
What we do
Manual VAPT for banks, fintechs, telecoms, government, ministries, healthcare and other regulated institutions across Africa. Every report is evidence-led and written by hand.
Consulting Services
Security Testing & Assessments
Manual Vulnerability Assessment and Penetration Testing (VAPT): web application, network, mobile, API, and cloud testing. Every report is evidence-led and written by hand, and one re-test round is included.
Learn moreBNR-Compliant Penetration Testing
Penetration testing and vulnerability assessments aligned to BNR Regulation N° 50/2022: the annual pentest, the twice-yearly assessments and a report ready to file with BNR, led by an OSCP-credentialled practitioner.
Learn moreManaged Security
Retained security advice between engagements: continuous external monitoring, vulnerability triage, fix verification and BNR-aligned guidance, at a cadence agreed with you. We do not run a 24/7 SOC.
Learn moreTraining & Workshops
Hands-on workshops for engineering and IT teams: secure-coding practice, phishing response, and incident handling grounded in real engagement findings.
Learn moreManaged Security
Two services we run inside a managed-security retainer: continuous external monitoring and security awareness.
How we work
Four steps, from the first call to the closure letter.
-
Scoping call
We map your environment, the rules you answer to and what needs testing
-
Proposal and SOW
A fixed price, scope, timeline and rules of engagement, within 48 hours of the call
-
Testing
1 to 6 weeks of manual testing with daily status updates on critical findings
-
Report and support
A written report with remediation guidance, one re-test round and a closure letter
What clients say
Security engagements, in our clients’ own words.
Its report explained each issue clearly for our technical team and our management, with reproduction steps and practical remediation guidance. IMIZI delivered the report ahead of the agreed deadline, presented the results in person at our offices, and verified all of our fixes in the re-test. We found IMIZI professional, careful with our production environment and data, and easy to work with. We would recommend IMIZI Cyber for penetration testing of financial services platforms.
IMIZI Cyber went above and beyond our expectations: thorough analysis, fantastic reports and follow-ups. I was relieved at how trustworthy they were and how well it all went. We'll surely be using them again.
IMIZI delivered a detailed report covering the identified issues, the business impact … and a prioritised remediation roadmap. The work was carried out professionally and confidentially.
From the blog
Guides to testing, regulation and security for regulated organisations across Africa.
How to scope a penetration testing RFP in Rwanda (with a tender checklist)
How to write a VAPT RFP or tender that selects a real penetration test: scope, vendor requirements, evaluation grid, timeline and a copy-paste checklist.
Penetration testing in Africa: a guide for regulated institutions
Our guide to penetration testing across Africa: the threat reality, the regulators in Nigeria, Ghana and South Africa alongside Rwanda and Kenya, manual VAPT compared with automated scanning, and how to choose a provider.
Penetration testing in Kenya: a guide for regulated institutions
A mobile-money-dominated market, CBK guidance, the Data Protection Act and ODPC, SACCOs and fintech: what real penetration testing looks like in Kenya, and how to choose a provider.
Common questions
Why do banks in Rwanda need penetration testing?
Do you help with BNR cybersecurity compliance?
How much does penetration testing cost in Rwanda?
What is BNR Regulation on cybersecurity?
What certifications does your lead practitioner hold?
How often should banks do penetration testing?
What is the difference between VAPT and penetration testing?
Do I need ISO 27001 certification in Rwanda?
Can you help us get ISO 27001, PCI DSS, or SOC 2 certified?
How do you handle our data during an engagement?
Do you offer cybersecurity training for employees?
Do you work with organisations outside Rwanda?
Scope your next regulatory test, tender or partner security review
Book a free 30-minute call. We map what needs testing against the rule you answer to (BNR, SWIFT CSP, Law N° 058/2021 or a partner's questionnaire) and send a fixed-price proposal within 48 hours of the call.
Get in touch
We respond within 24 hours.